Introduction
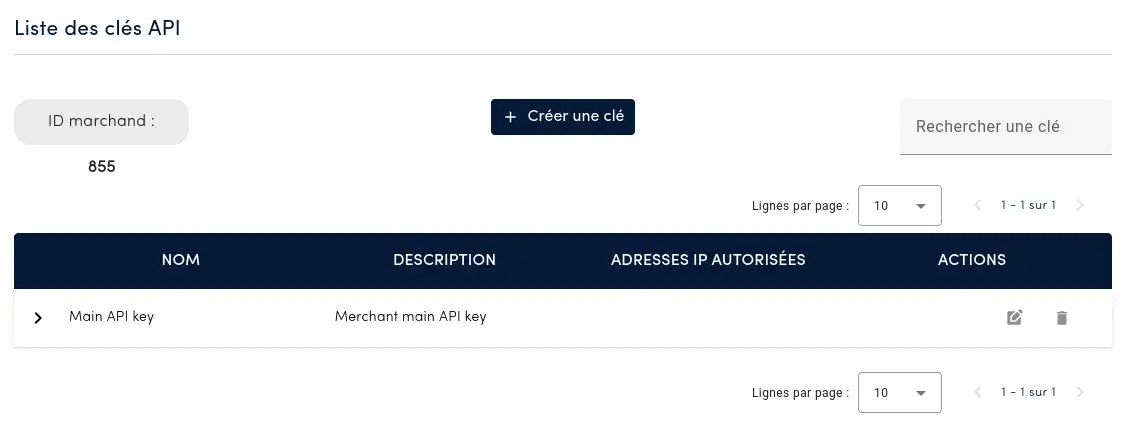
API keys are the main authentication mechanism of the HUB2 API. Understanding what they are and how to use them is essential. API keys are managed on the HUB2 Dashboard, in the “Developer” section, as illustrated below: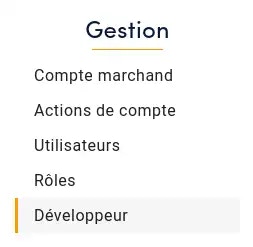
Key management
Creating a key
1
Create a key
Click the “Create a key” button to open the following window: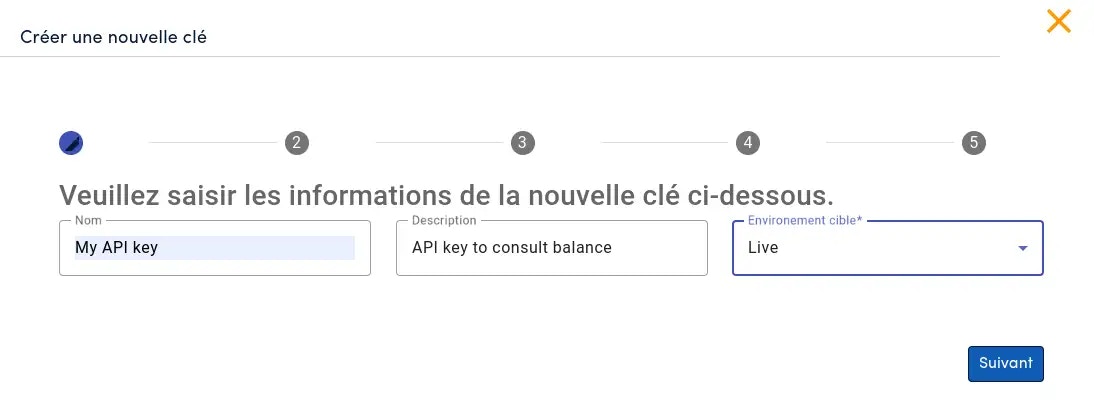
2
Details
- (Optional) Enter a name and a description for the new key.
- The environment (sandbox or live) is required. The new key is restricted to this environment. Read more about environments.
3
IP Whitelist
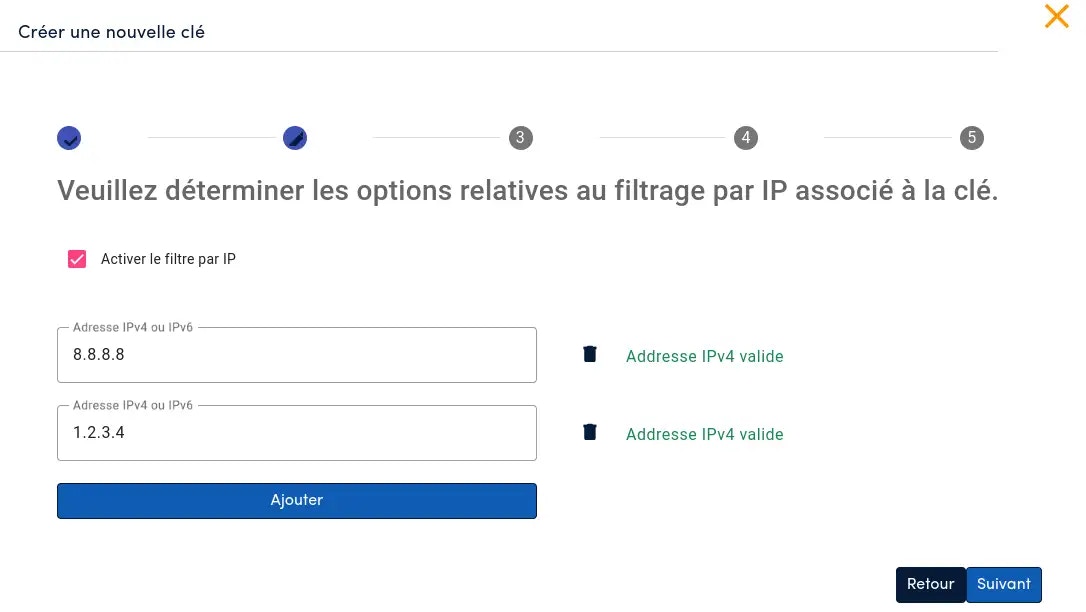
4
Permissions
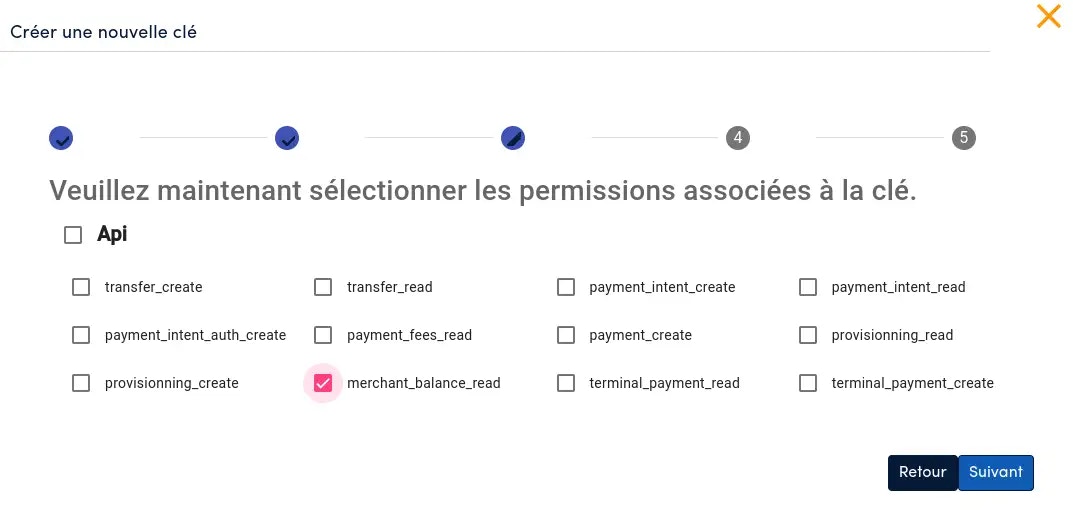
5
Review and validate
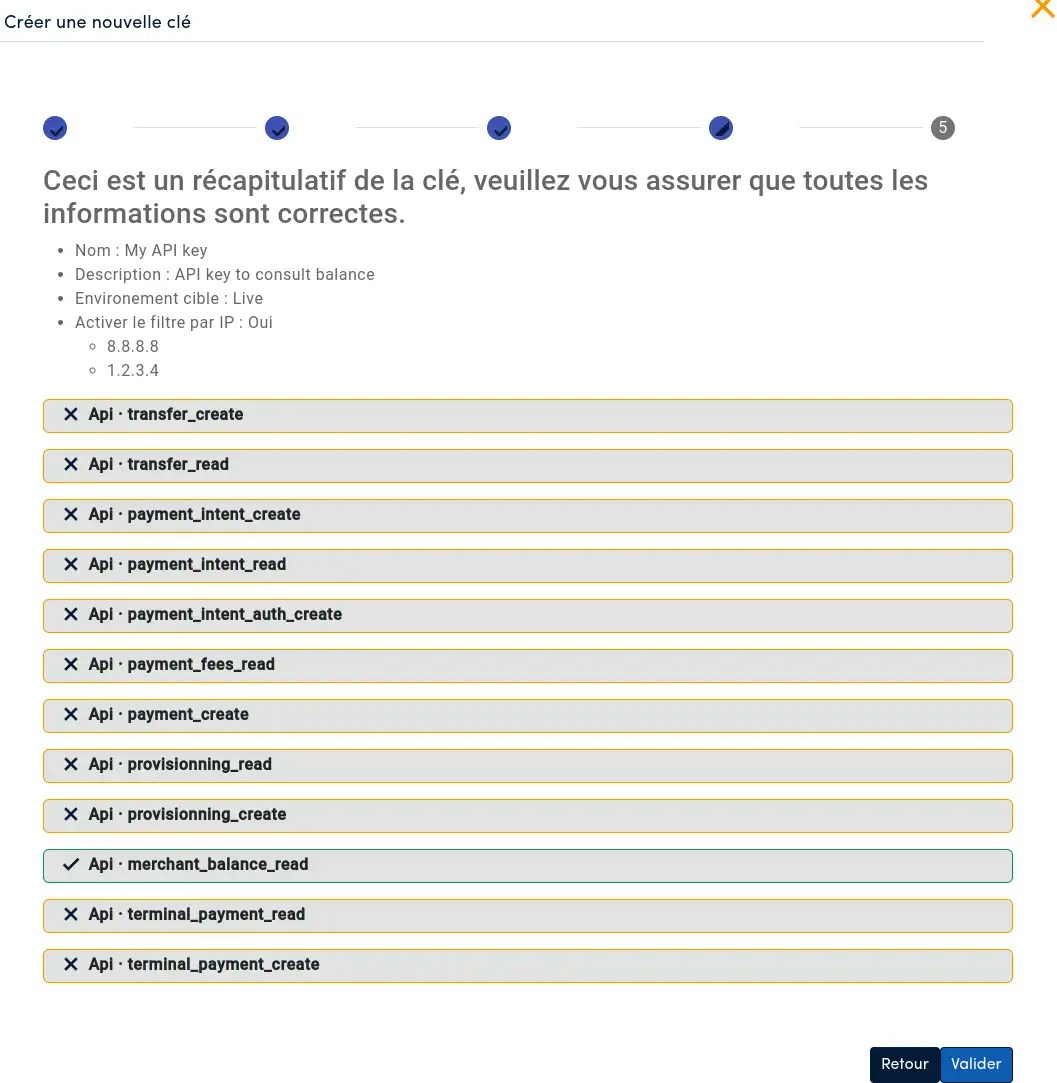
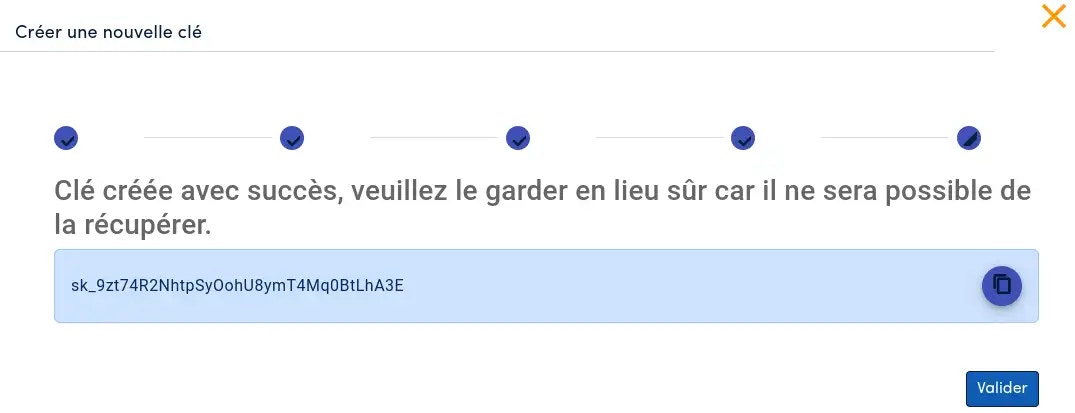
Editing a key
On each API key row, in the “Actions” column, an Edit button lets you change the settings of a key. Editing follows the same steps as creation, except that the key itself cannot be viewed. Every setting can be edited.Deleting a key
In the “Actions” column, a Delete button lets you delete a key.Using the keys
The API reference shows which endpoints require authentication. For these endpoints, set the following HTTP headers on every request to identify and authenticate the sender:API key configuration
Environment
sandbox: a closed environment for integration testing. No real transaction is created when the API key is set to thesandboxenvironment: HUB2 simulates provider behaviour, andsandboxtransactions use thesandboxtransfer and collection accounts.live: the real-world environment. Alivekey processes real traffic, and providers are contacted when the transaction endpoints are called. Sending traffic in theliveenvironment requires the GO LIVE and an integration review by HUB2.
IP address restriction
IP address restriction is an optional feature that further secures exchanges between the merchant platform and HUB2. When an IP address restriction is set on an API key, HUB2 checks that the IP address sending the HTTP request is authorized to use the API key it contains.Permissions
Permissions are configured per API key, so a merchant can create several keys with different permissions, each with its own responsibility. An API key must carry at least one API permission. A call to an endpoint whose permission the key lacks is rejected with403 and the error code missing_permission.
The permissions and their descriptions are as follows. In the Dashboard, they are grouped under Api and listed by the part after Api. (for example transfer_create).